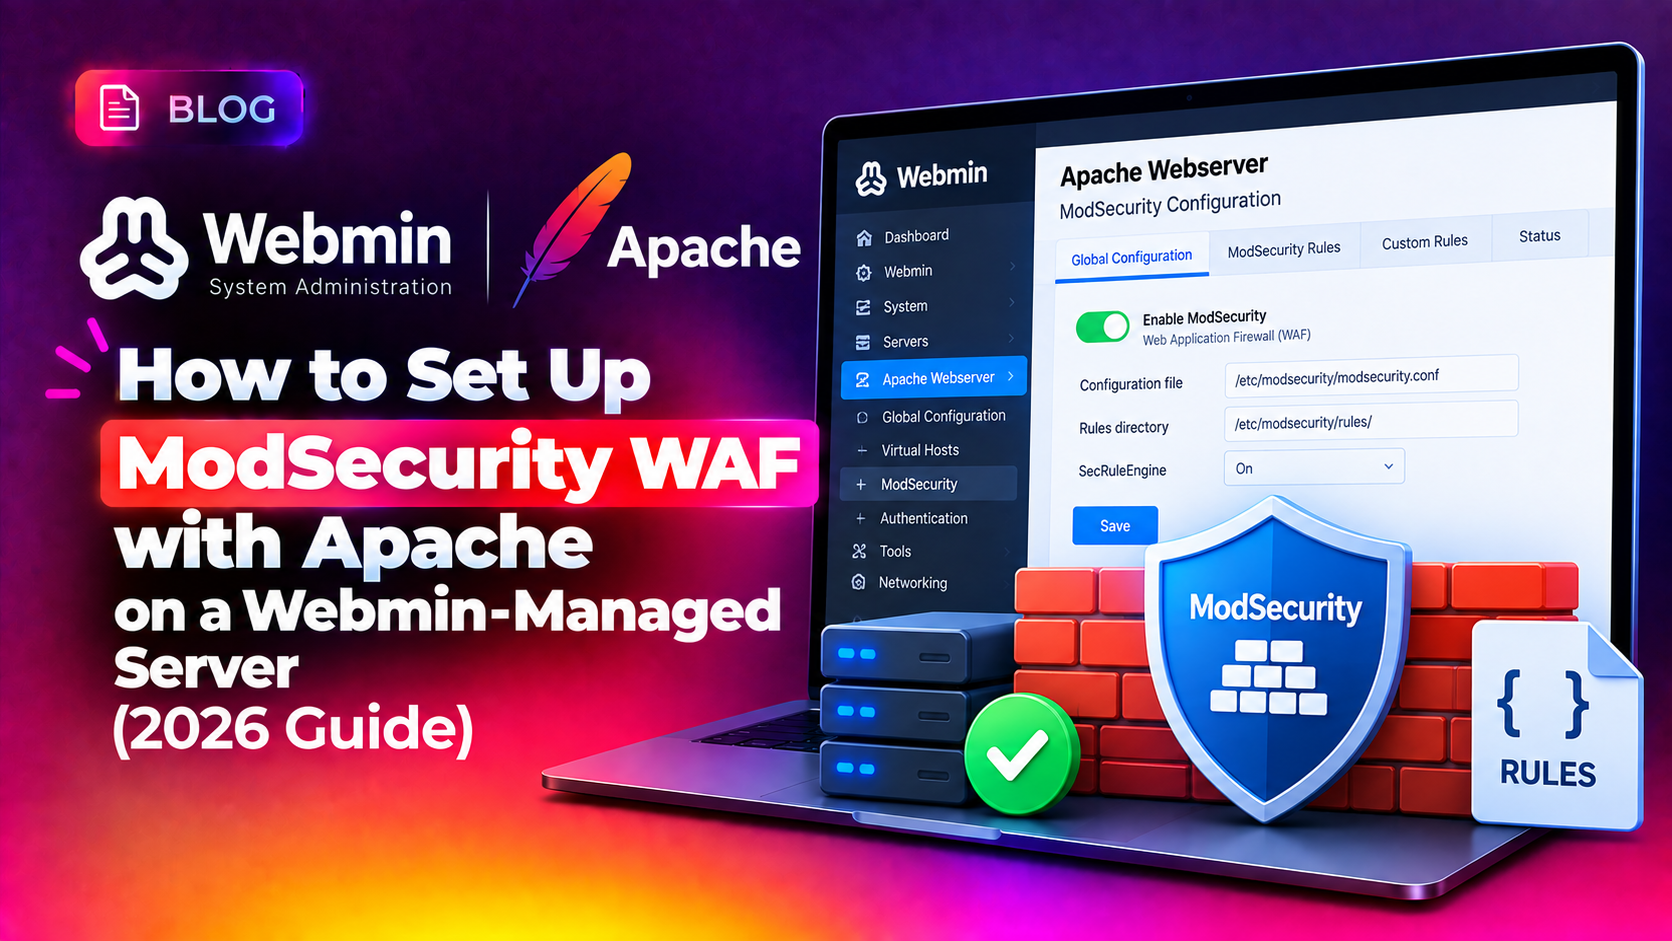
If you manage a Linux server through Webmin, you already have firewall rules, fail2ban jails, and maybe two-factor authentication locked down. But none of those tools inspect what actually happens inside an HTTP request. A webmin modsecurity waf setup closes that gap by adding a Layer-7 web application firewall that reads every request hitting Apache and blocks SQL injection, cross-site scripting, path traversal, and malicious bot traffic before it ever reaches your website's code.
This guide walks through installing ModSecurity with the OWASP Core Rule Set (CRS) on a Webmin-managed Apache server, configuring it safely in detection mode first, switching to full blocking, and tuning out false positives without turning off protection site-wide.
Why Firewalls and fail2ban Aren't Enough
UFW, iptables, and CSF operate at the network layer — they block or allow traffic based on IP address and port. fail2ban watches log files and bans IPs after repeated failed logins. Neither of these tools looks at the content of a legitimate-looking HTTP GET or POST request.
That means an attacker can send a perfectly normal-looking request to /login.php?id=1' OR '1'='1 straight through your firewall, because from the network's perspective it's just allowed traffic on port 443. A web application firewall like ModSecurity is what actually reads that query string and recognizes the SQL injection pattern.
- Firewalls — block by IP/port (network layer)
- fail2ban — blocks by repeated auth failures (log layer)
- ModSecurity WAF — blocks by request content (application layer)
Running all three together is what a properly hardened, Webmin-managed server looks like in 2026.
💡 None of these worked? Skip the guesswork.
Get Expert Help →Step 1: Install ModSecurity and the OWASP Core Rule Set
SSH into your server (Webmin's built-in terminal module works fine for this) and install the packages. On Ubuntu/Debian:
sudo apt update
sudo apt install apache2 libapache2-mod-security2 modsecurity-crs
On RHEL/CentOS/AlmaLinux (common on cPanel and Webmin-managed boxes):
sudo dnf install httpd mod_security mod_security_crsEnable security2 and unique_id, then restart Apache:
sudo a2enmod security2 unique_id
sudo systemctl restart apache2ModSecurity ships with a template config that is safe to use as a baseline:
sudo cp /etc/modsecurity/modsecurity.conf-recommended /etc/modsecurity/modsecurity.confYou can verify the module loaded correctly from Webmin itself: go to Webmin → Servers → Apache Webserver → Global configuration and confirm mod_security2 appears in the loaded modules list.
Once you've reviewed at least a few days of audit logs and confirmed there are no obvious false positives on core workflows, switch the rule engine on:
sudo sed -i 's/^SecRuleEngine DetectionOnly/SecRuleEngine On/' /etc/modsecurity/modsecurity.conf
sudo systemctl restart apache2Never disable a rule ID across the entire server unless you're certain it has no security value for you. Instead, scope the exclusion to the specific URI that triggered it. Add this inside the relevant <Location> or <Directory> block, after the CRS include line in your Apache virtual host config:
<LocationMatch "/wp-admin/admin-ajax.php">
    SecRuleRemoveById 941100
</LocationMatch>
For a global exception (used sparingly, only for rules you've confirmed are never useful in your environment):
SecRuleRemoveById 941100Restart Apache and repeat the action that previously triggered the false positive. It should now succeed while the rest of the CRS ruleset continues blocking everything else.
Step 5: Test That the WAF Is Actually Blocking Attacks
Confirm ModSecurity is live by sending a harmless SQL injection test string against your own domain:
curl -s -o /dev/null -w "%{http_code}\n" "https://yourdomain.com/?id=1' OR '1'='1"A response of 403 confirms ModSecurity and the CRS are actively blocking malicious-looking requests. If you get 200 instead, double-check that:
SecRuleEngineis set toOn, notDetectionOnly- Apache was actually restarted after the config change
- The CRS include file is loaded, typically via
/usr/share/modsecurity-crs/owasp-crs.loador an equivalentIncludedirective in your Apache config
Step 6: Monitor Ongoing Activity from Webmin
Once the WAF is live, treat the audit log the same way you'd treat fail2ban's ban log — check it periodically for patterns. You can use Webmin's System Logs module to add /var/log/modsec_audit.log as a monitored log file, or pair it with Logwatch for a daily digest emailed to your team.
If your server also runs cPanel/WHM alongside Webmin for certain accounts, note that cPanel ships its own ModSecurity Vendor Rules interface — but a standalone Webmin-managed Apache box needs the manual setup covered above.
If your team is managing this across dozens of servers, our server hardening service handles WAF deployment, rule tuning, and ongoing false-positive monitoring so nothing breaks silently in production.
Common Mistakes to Avoid
- Skipping detection-only mode — jumping straight to
SecRuleEngine Onis the #1 cause of broken login forms, checkout pages, and file uploads. - Disabling entire rule categories instead of scoping exceptions to a specific URI — this reopens the exact attack surface you were trying to close.
- Forgetting to restart Apache after every config change — ModSecurity directives only take effect after a reload.
- Never reviewing the audit log after go-live — new false positives appear whenever you deploy new application features.
- Running an outdated CRS version — the rule set is updated regularly to cover newly discovered attack patterns; check for updates quarterly.
Understanding OWASP CRS Paranoia Levels
The OWASP Core Rule Set ships with four paranoia levels (PL1-PL4), each adding progressively stricter pattern matching. Most webmin modsecurity waf setup guides skip this entirely, but it directly controls how many false positives you'll fight.
- PL1 (default) - catches obvious, high-confidence attacks with minimal false positives. Recommended starting point for production sites.
- PL2 - adds broader coverage for XSS and SQLi variants; expect a noticeable increase in false positives on complex applications.
- PL3-PL4 - extremely strict, generally reserved for high-security environments like payment processing, and require significant tuning time before going live.
Set the paranoia level in /etc/modsecurity/crs/crs-setup.conf:
SecAction "id:900000,phase:1,nolog,pass,t:none,setvar:tx.paranoia_level=1"Stay at PL1 until you've fully cleared the audit log of false positives, then consider stepping up only if your threat model genuinely requires it.
Excluding False Positives Per Application
If your Webmin-managed server hosts multiple sites - a WordPress blog, a custom PHP application, and an API - a single global exception list won't work cleanly across all of them. The OWASP CRS project maintains ready-made exclusion rule packages for common platforms including WordPress, Joomla, Drupal, cPanel, and Nextcloud, which pre-emptively exclude known-safe patterns for those specific applications.
Install the WordPress exclusion package on Debian/Ubuntu:
sudo apt install modsecurity-crs-wordpressThen include it in your Apache config after the main CRS include, but before any custom rules you've written:
IncludeOptional /usr/share/modsecurity-crs/rules/*.conf
IncludeOptional /usr/share/modsecurity-crs/plugins/wordpress-rule-exclusions-before.conf
This dramatically cuts down manual tuning time compared to hunting down every WordPress admin-ajax false positive by hand.
Pairing ModSecurity with fail2ban for Automated Banning
By default, ModSecurity blocks a single malicious request but doesn't ban the IP that sent it - the same attacker can keep probing with new payloads. You can close this gap by feeding ModSecurity's audit log into fail2ban, so repeat offenders get banned at the firewall level automatically.
Create a fail2ban filter at /etc/fail2ban/filter.d/modsecurity.conf:
[Definition]
failregex = \[client <HOST>\] ModSecurity: Access denied
ignoreregex =
Then enable a matching jail in /etc/fail2ban/jail.local:
[modsecurity]
enabled = true
port = http,https
filter = modsecurity
logpath = /var/log/apache2/error.log
maxretry = 5
bantime = 3600
Restart fail2ban to apply it:
sudo systemctl restart fail2banNow any IP that trips five ModSecurity rule matches gets banned at the firewall for an hour - combining application-layer detection with network-layer enforcement.
Performance and Resource Considerations
On a low-memory VPS (1-2GB RAM), running the full CRS ruleset with PL1 is typically fine, but a few settings help keep resource usage predictable:
- Set
SecRequestBodyLimitandSecResponseBodyLimitinmodsecurity.confto reasonable values (e.g. 13MB request, 1MB response) to avoid excessive memory use on large file uploads. - Disable response body inspection (
SecResponseBodyAccess Off) unless you specifically need to scan outbound content - this alone noticeably reduces overhead. - Rotate the audit log regularly with
logrotate; unbounded audit logs on a busy site can grow into gigabytes within weeks.
A properly tuned ModSecurity WAF is one of the highest-value additions you can make to a Webmin-managed server's security stack — it catches the exact class of attacks that firewalls and fail2ban were never designed to see. Combined with the SSH hardening, 2FA, and firewall configuration you've likely already set up, it closes the loop on Layer-7 protection.