Why Your Ubuntu PPA or Repository Stops Working
Adding a third-party PPA or repository is one of the first things Ubuntu users do — to get the latest Firefox ESR, a newer version of GIMP, or a proprietary driver. But in 2026 on Ubuntu 24.04 LTS (Noble Numbat) and 24.10/25.04, it breaks more often than it used to.
The root cause is a security overhaul that Ubuntu completed with 24.04: the old apt-key tool is gone, the shared /etc/apt/trusted.gpg keyring is no longer trusted by default, and every repository must now be individually signed using the signed-by attribute. If any of that is missing or wrong, apt update fails with cryptic errors.
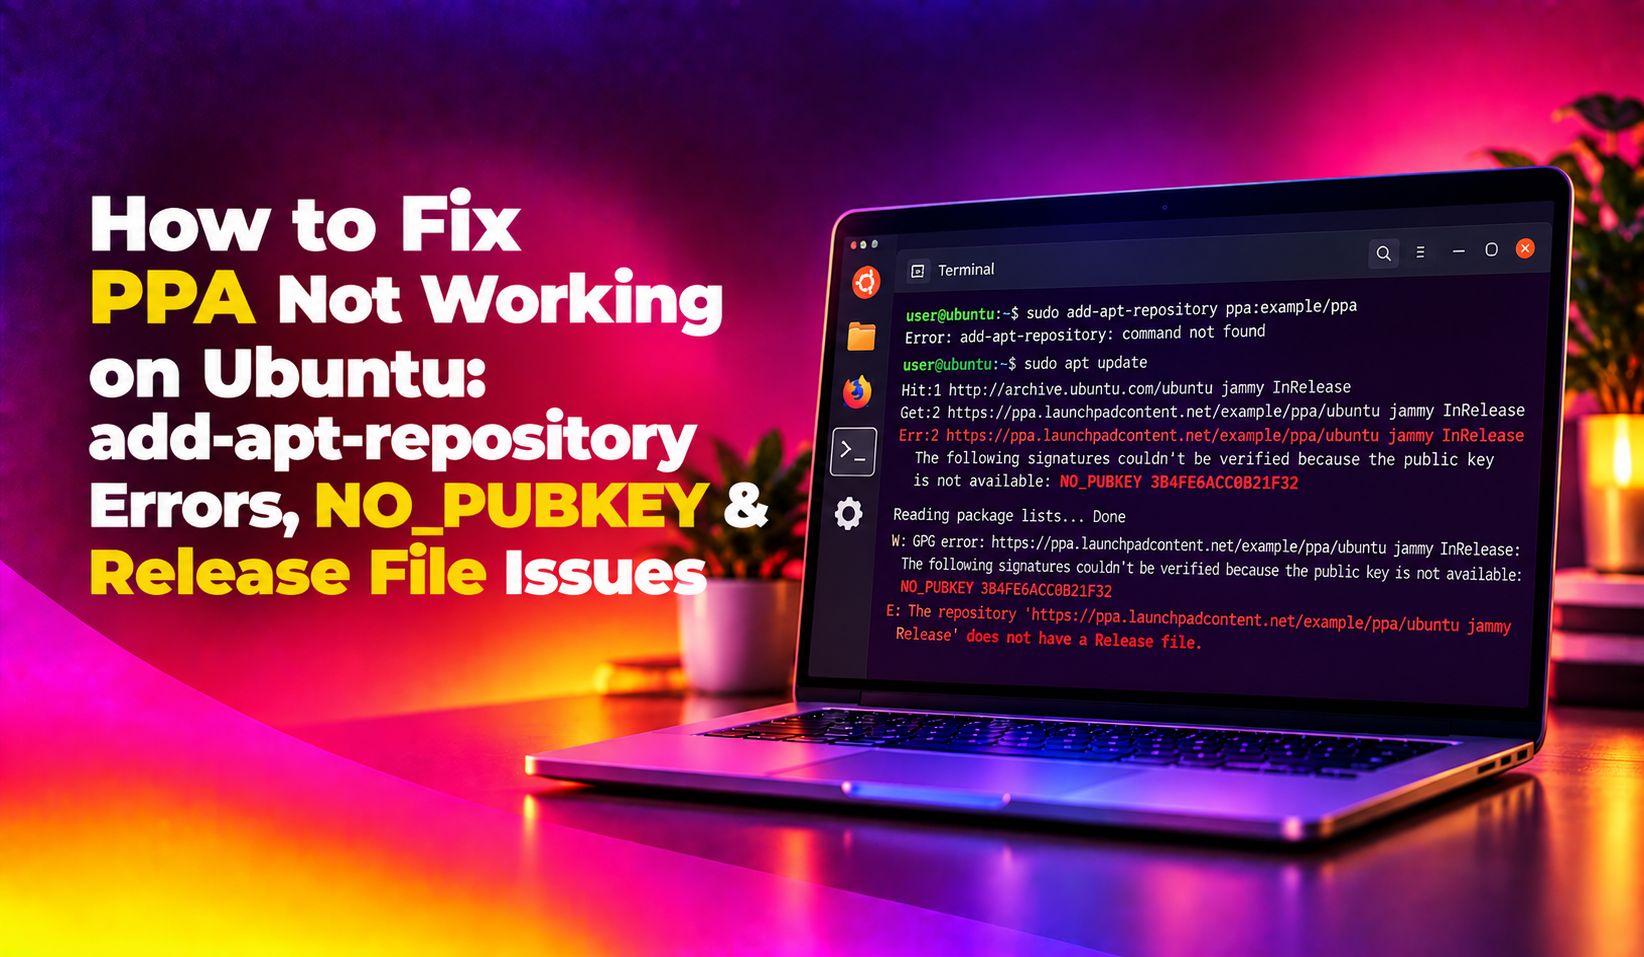
This guide walks you through every common error — NO_PUBKEY, Repository does not have a Release file, add-apt-repository: command not found, certificate verification failed — with exact commands to fix each one.
Error 1: add-apt-repository: command not found
This happens on minimal Ubuntu installs (servers, WSL, fresh cloud images) because the helper package isn't included by default.
Fix:
sudo apt update
sudo apt install -y software-properties-common
After installing, retry your add-apt-repository ppa:... command. If you are on Ubuntu 24.04 and the PPA was created for an older release (focal, jammy), the next step may still fail — keep reading.
Error 2: "Repository Does Not Have a Release File"
Full error:
E: The repository 'http://ppa.launchpad.net/some-user/some-ppa/ubuntu noble Release'
   does not have a Release file.
This means the PPA maintainer has not published a Noble (24.04) build of their packages. The PPA exists for Jammy (22.04) or Focal (20.04) only.
Step 1 — Confirm which releases the PPA supports. Open a browser and visit:
https://launchpad.net/~{ppa-owner}/{ppa-name}/+packagesLook for "noble" in the series column. If it's absent, the PPA simply does not support your Ubuntu version.
Step 2 — Remove the broken PPA:
sudo add-apt-repository --remove ppa:some-user/some-ppa
sudo apt update
Step 3 — Force an older series (risky, only for experienced users). If you understand the risks and the packages are compatible, you can manually create the source pointing to the last supported series:
echo "deb [signed-by=/etc/apt/keyrings/some-ppa.gpg] http://ppa.launchpad.net/some-user/some-ppa/ubuntu jammy main" | sudo tee /etc/apt/sources.list.d/some-ppa.listThen import the key as described in the next section.
Error 3: NO_PUBKEY — GPG Key Not Trusted
Full error:
W: GPG error: http://ppa.launchpad.net/some-user/some-ppa/ubuntu noble InRelease:
   The following signatures couldn't be verified because the public key is
   not available: NO_PUBKEY 3B4FE6ACC0B21F32
This happens when a repository's key is either missing entirely or sitting in the deprecated /etc/apt/trusted.gpg keyring, which Ubuntu 24.04 no longer consults.
Modern Fix (Ubuntu 24.04+ method)
The correct 2026 approach is to save each key in its own .gpg file inside /etc/apt/keyrings/ and reference it with signed-by.
Step 1 — Create the keyrings directory if it doesn't exist:
sudo mkdir -p /etc/apt/keyringsStep 2 — Download the key from Ubuntu's keyserver and convert it to binary format:
sudo gpg --no-default-keyring   --keyring /tmp/tmp-keyring.gpg   --keyserver keyserver.ubuntu.com   --recv-keys 3B4FE6ACC0B21F32

sudo gpg --no-default-keyring   --keyring /tmp/tmp-keyring.gpg   --export --output /etc/apt/keyrings/some-ppa.gpg

sudo rm /tmp/tmp-keyring.gpg
sudo chmod 644 /etc/apt/keyrings/some-ppa.gpg
(Replace 3B4FE6ACC0B21F32 with the key ID from your actual error message.)
Step 3 — Update or create the sources list file with the signed-by attribute:
sudo nano /etc/apt/sources.list.d/some-ppa.listChange any line that looks like:
deb http://ppa.launchpad.net/some-user/some-ppa/ubuntu noble mainTo:
deb [signed-by=/etc/apt/keyrings/some-ppa.gpg] http://ppa.launchpad.net/some-user/some-ppa/ubuntu noble mainStep 4 — Test:
sudo apt updateThe NO_PUBKEY warning should be gone.
Error 4: "Key Is Stored in Legacy trusted.gpg Keyring" Warning
Ubuntu 24.04 prints this warning for every key that was previously added via apt-key add and now lives in /etc/apt/trusted.gpg:
W: http://packages.example.com/ubuntu/dists/noble/InRelease:
   Key is stored in legacy trusted.gpg keyring
   (/etc/apt/trusted.gpg), see the DEPRECATION section
   in apt-key(8) for details.
This is a warning, not a hard failure — apt still works. But you should migrate these keys.
Step 1 — List which keys are in the legacy keyring:
sudo apt-key listNote the 8-character key ID at the end of the fingerprint line (e.g., ABCD1234).
Step 2 — Export each key to the modern location:
sudo apt-key export ABCD1234   | sudo gpg --dearmor   | sudo tee /etc/apt/keyrings/example.gpg > /dev/null
sudo chmod 644 /etc/apt/keyrings/example.gpg
Step 3 — Remove the key from the legacy keyring:
sudo apt-key del ABCD1234Step 4 — Add signed-by to the repository source file as described in the previous section.
Error 5: "Certificate Verification Failed" on apt update
Full error:
E: Certificate verification failed: The certificate is NOT trusted.
   The certificate chain uses expired certificate.
This is caused by an out-of-date ca-certificates package or a wrong system clock.
Check your system clock:
timedatectl statusIf the time is wrong, sync it:
sudo timedatectl set-ntp true
sudo systemctl restart systemd-timesyncd
Update CA certificates:
sudo apt install --reinstall ca-certificates
sudo update-ca-certificates
If you are behind a corporate proxy with SSL inspection, you will need to import the proxy's root CA into the system trust store and into /etc/apt/apt.conf.d/.
Error 6: "Conflicting Values Set for Option Signed-By" After Upgrade
After upgrading from Ubuntu 22.04 to 24.04, some source files may have duplicate or conflicting signed-by references:
E: Conflicting values set for option Signed-By
   regarding source https://packages.example.com/ noble:
   /usr/share/keyrings/example-archive-keyring.gpg !=
   /etc/apt/keyrings/example.gpg
The fix is to ensure all .list and .sources files for that repository use the same key path. Check both locations:
grep -r "signed-by" /etc/apt/sources.list.d/
grep -r "signed-by" /etc/apt/sources.list
Edit the conflicting file to point to a single key file:
sudo nano /etc/apt/sources.list.d/example.listChoose one key path, delete the duplicate file, and re-run sudo apt update.
How to Add a New PPA Correctly on Ubuntu 24.04 (2026 Method)
For PPAs hosted on Launchpad, add-apt-repository still handles the key automatically on 24.04 — it now writes the key to /etc/apt/keyrings/ by default:
sudo add-apt-repository ppa:some-user/some-ppa
sudo apt update
For third-party repos that provide their own key URL, the modern pattern is:
# 1. Download and convert the key
curl -fsSL https://example.com/repo-key.gpg   | sudo gpg --dearmor   -o /etc/apt/keyrings/example.gpg
sudo chmod 644 /etc/apt/keyrings/example.gpg

# 2. Add the repo source with signed-by
echo "deb [arch=amd64 signed-by=/etc/apt/keyrings/example.gpg]   https://packages.example.com/ubuntu noble main"   | sudo tee /etc/apt/sources.list.d/example.list

# 3. Update
sudo apt update
This avoids all legacy keyring warnings on current and future Ubuntu versions.
Quick Diagnostic Checklist
Run these commands to get a full picture of your APT configuration health:
# Check for all apt errors in one pass
sudo apt update 2>&1 | grep -E "^(E:|W:)"

# List all currently configured repositories
grep -r "^deb" /etc/apt/sources.list /etc/apt/sources.list.d/

# Check keys in both keyrings
sudo apt-key list 2>/dev/null
ls -la /etc/apt/keyrings/
ls -la /usr/share/keyrings/

# Verify a specific key fingerprint
gpg --show-keys /etc/apt/keyrings/example.gpg
If you're still stuck after working through these steps, our team at professional desktop support can remotely diagnose your exact APT configuration and resolve it in minutes.
Frequently Asked Questions
Is it safe to use a PPA designed for Ubuntu 22.04 on Ubuntu 24.04?
Only if the PPA maintainer has published Noble (24.04) builds. Forcing a Jammy (22.04) PPA onto Noble can cause dependency conflicts and broken upgrades. Always verify on the Launchpad packages page first.
What's the difference between /etc/apt/keyrings/ and /usr/share/keyrings/?
Both are valid locations for signed-by keys. /usr/share/keyrings/ is typically used by software packages that ship their own key (managed by the package manager). /etc/apt/keyrings/ is the preferred location for keys you add manually — it survives package upgrades.
Can I still use apt-key on Ubuntu 24.04?
No. apt-key was removed entirely in Ubuntu 24.04. Any command using apt-key add will fail with "command not found". Use the gpg --dearmor + signed-by workflow instead.
Why does apt update show NO_PUBKEY even though I already imported the key?
The key is likely in the legacy /etc/apt/trusted.gpg keyring or in /usr/share/keyrings/ but the .list file is missing the signed-by attribute. Ubuntu 24.04 will not use keys from those locations unless signed-by explicitly points to them.
How do I completely remove a PPA and all packages installed from it?
Install ppa-purge first: sudo apt install ppa-purge. Then run: sudo ppa-purge ppa:some-user/some-ppa. This removes the repository, downgrades or removes packages that came from it, and deletes the key from your system.