SaaS billing platforms sit at the intersection of recurring revenue and recurring risk: every invoice, card token, and webhook payload that moves through your infrastructure touches cardholder data. SSL installation for SaaS billing platforms is not the same task as securing a marketing site — it means wildcard coverage across tenant subdomains, automated renewal so a lapsed certificate never breaks a webhook, and a certificate chain that satisfies PCI DSS auditors on demand. Get it wrong and you risk a failed PCI scan, a broken payment gateway integration, or a multi-tenant outage that takes down every customer at once.
This guide breaks down what proper SSL installation and certificate lifecycle management actually looks like for billing and payments platforms in 2026 — including costs, provider evaluation criteria, and the automation patterns that keep renewal from ever becoming a fire drill.
Why SSL Installation Matters More for SaaS Billing Platforms
A generic SaaS app can tolerate a short SSL hiccup. A billing platform cannot. When your infrastructure processes, stores, or transmits credit card data, PCI DSS compliance makes SSL/TLS installation a hard requirement, not a best practice. PCI DSS v4 mandates TLS 1.2 or higher for all cardholder-data transmission, disabling of weak or deprecated protocols, and demonstrable evidence that certificates are actively monitored and renewed — not just installed once and forgotten.
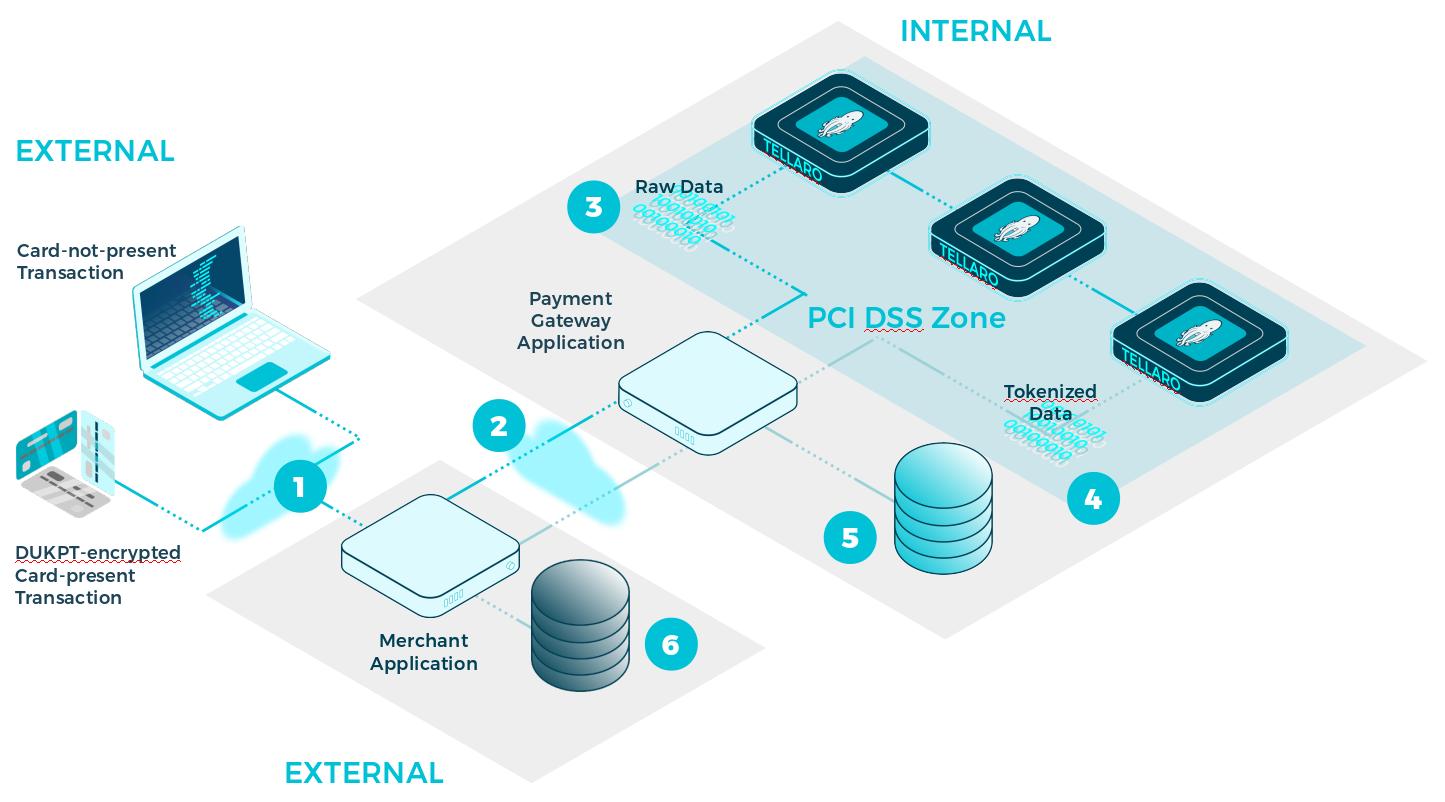
Billing platforms also run on infrastructure that regular web apps don't have to worry about:
- Multi-tenant subdomains — each customer or merchant account often gets its own subdomain (billing.customer1.yourapp.com), multiplying the number of certificates that need coverage.
- Webhook endpoints — payment processors like Stripe, Braintree, and Adyen validate your webhook TLS certificate before delivering events; an expired cert silently breaks payment reconciliation.
- PCI scan windows — quarterly ASV scans check certificate validity, chain completeness, and protocol strength; a single expired or misconfigured certificate can fail the entire scan.
- Customer trust signals — billing pages are exactly where users check for the padlock icon before entering card details.
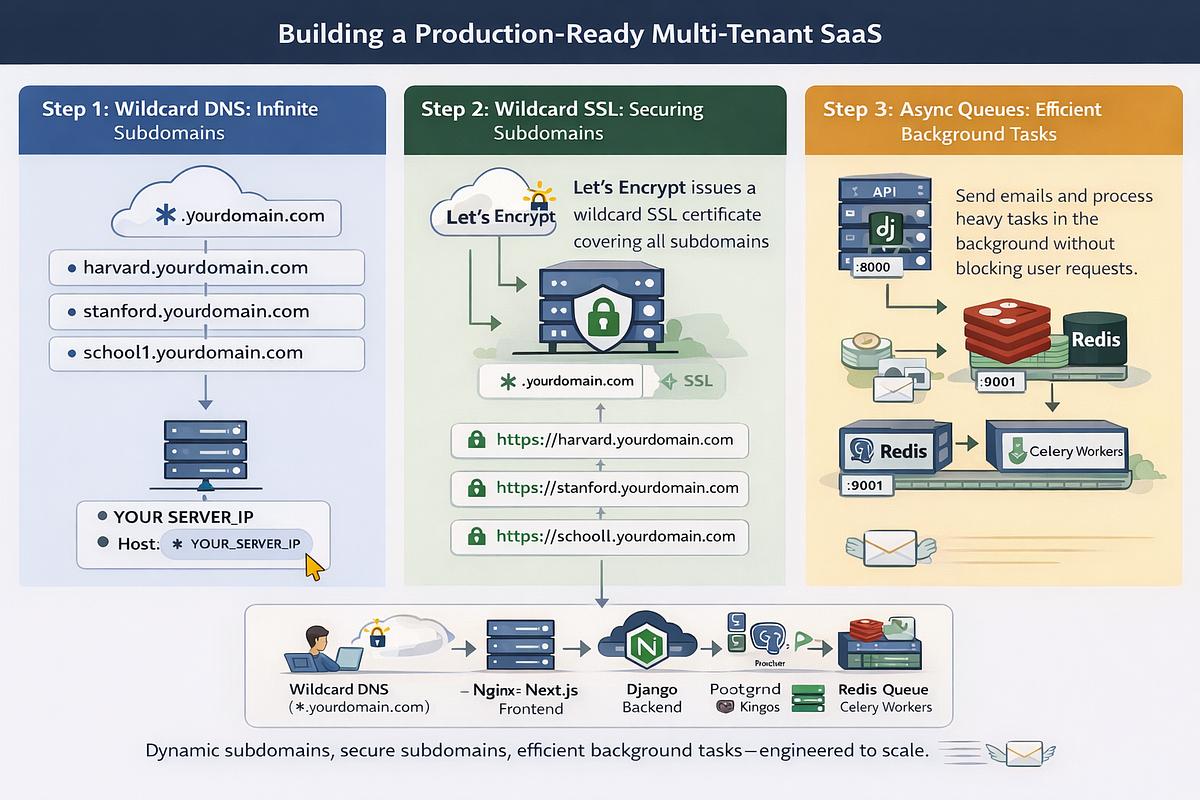
A single lapsed certificate on a billing platform isn't just a browser warning — it's a potential compliance violation, a broken integration, and a trust event with paying customers all at once.
How Much Does SSL Installation and Management Cost in 2026?
Costs vary depending on certificate type, the number of domains/subdomains you need to cover, and whether you're paying for one-time installation or ongoing lifecycle management.
| Approach | Typical Cost (2026) | Best For |
|---|---|---|
| Free ACME/Let's Encrypt cert, manual renewal | $0 + engineering time | Single-domain apps, low compliance stakes |
| Free ACME cert with automated renewal (self-managed) | $0–$150/mo in engineering/tooling time | Small SaaS teams comfortable maintaining scripts |
| Wildcard SSL cert, single provider | $50–$300/year per wildcard cert | Multi-tenant apps with subdomain-per-customer architecture |
| Managed SSL/certificate lifecycle service (CloudHouse and similar) | $150–$800/mo depending on domain count | Billing platforms needing PCI-ready monitoring and 24/7 renewal coverage |
| Enterprise PKI / Extended Validation setup | $1,000+/year | Large payment platforms with strict brand and compliance requirements |
The real cost of SSL for a billing platform isn't the certificate itself — a wildcard certificate can cost less than $200/year. It's the operational cost of monitoring, rotation, and renewal automation across every subdomain, load balancer, and CDN edge, which is exactly where in-house teams under-invest until an outage forces the issue.
What to Look for in an SSL Installation Provider for Billing Platforms
Most SSL installation guides walk through a generic certbot command and call it done. For a payments platform, that misses the parts that actually matter: multi-tenant scale, PCI evidence trails, and renewal automation that doesn't depend on someone remembering a calendar reminder. Use this checklist when evaluating a provider:
- Wildcard and SAN certificate support — can they issue and manage wildcard certs across all your tenant subdomains from one certificate authority relationship?
- Automated renewal with DNS-01 validation — do they integrate with your DNS provider's API (Cloudflare, Route 53, etc.) so renewals happen without manual TXT record updates?
- PCI DSS documentation support — can they provide audit-ready logs showing certificate issuance, renewal history, and protocol configuration for your ASV scans?
- Expiry monitoring and alerting — proactive alerts well before expiry, not just a renewal script that might silently fail.
- Load balancer / CDN distribution — experience installing and rotating certificates across your specific stack (Nginx, HAProxy, AWS ALB, Cloudflare, etc.) without downtime.
- Response time for emergency renewals — what happens if a renewal fails at 2 a.m. and your webhook endpoint starts rejecting payment processor traffic?
- Hourly or flexible billing — avoid providers that lock you into large annual retainers for what should be a well-defined, mostly automated task.
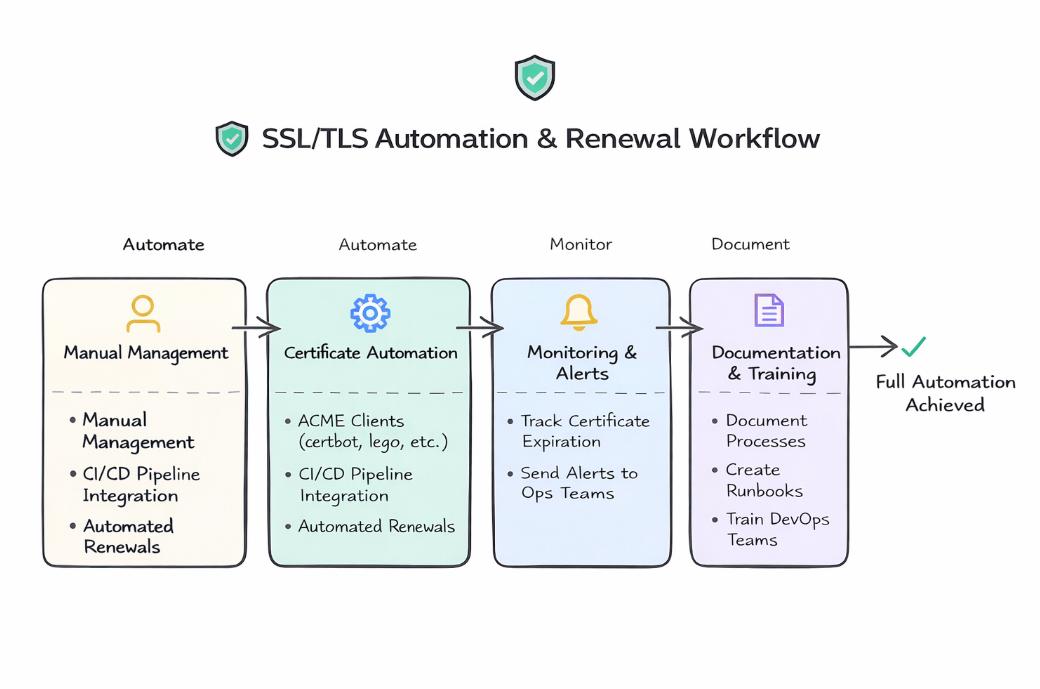
Providers offering SSL installation and server hardening as part of a broader security engagement typically catch configuration issues — like weak cipher suites or incomplete certificate chains — that a bare-bones cert reseller never checks.
In-House vs Outsourced SSL Management: Which Is Right for Your SaaS?
Engineering leads often default to handling SSL in-house because the initial installation feels simple. The real cost shows up months later, at 2 a.m., when a renewal job silently fails.
| Factor | In-House | Outsourced / Managed |
|---|---|---|
| Initial setup time | Days, depending on team SSL/DevOps experience | Hours — providers already have wildcard/multi-tenant playbooks |
| Renewal reliability | Depends entirely on internal scripts/cron jobs staying healthy | Monitored and alerted 24/7 by a dedicated team |
| PCI audit readiness | You build and maintain your own evidence trail | Provider supplies audit-ready renewal and configuration logs |
| Multi-tenant scaling | Requires custom tooling as tenant count grows | Wildcard and SAN cert strategy built in from day one |
| Cost predictability | Hidden cost in engineer hours spent firefighting | Fixed monthly or hourly billing, no surprise outages |
| Best fit | Teams with dedicated DevOps/security engineers and low domain count | Growing billing platforms with multiple tenant subdomains and compliance obligations |
For a small SaaS with one domain, in-house ACME automation is often fine. Once you're managing wildcard certs across dozens of tenant subdomains, load balancers, and a PCI compliance calendar, the operational overhead of doing it in-house usually costs more in engineering time than an outsourced SSL installation and management retainer.
Why SaaS Billing Platforms Choose CloudHouse for SSL Installation
CloudHouse works with SaaS and billing platforms that can't afford a lapsed certificate breaking a payment integration. Our team handles wildcard and multi-tenant SSL installation, sets up automated DNS-01 renewal pipelines tied to your existing DNS provider, and maintains the audit trail your PCI assessor will ask for — all on hourly or flexible monthly billing with no long-term lock-in. Support is available around the clock, so a failed renewal at 2 a.m. gets fixed before it becomes a payment outage, not after.
Frequently Asked Questions
How much does SSL certificate management cost for a SaaS billing platform?
Expect $150–$800 per month for managed certificate lifecycle services depending on the number of domains and subdomains you're covering, versus $50–$300 per year for a self-managed wildcard certificate alone. The bulk of the cost difference is monitoring, renewal automation, and PCI-ready documentation rather than the certificate itself.
Do I need a wildcard SSL certificate for a multi-tenant SaaS platform?
In most cases, yes. A wildcard SSL certificate for multi-tenant SaaS lets you secure unlimited tenant subdomains under one certificate instead of issuing and renewing a separate cert per customer, which becomes unmanageable once you pass a handful of tenants.
How long does SSL installation take for a billing platform?
Straightforward single-domain installation can take a few hours. Multi-tenant setups involving wildcard certificates, load balancer configuration, and DNS-01 automation typically take one to three business days to configure and test properly.
Does SSL installation alone make a billing platform PCI compliant?
No. SSL/TLS installation satisfies the encryption-in-transit requirement of PCI DSS, but full compliance also requires secure storage of cardholder data, access controls, logging, and regular vulnerability scans. Proper certificate management is a necessary piece of PCI compliance, not the whole picture.
Do you offer a trial or month-to-month plan for SSL management?
Yes. CloudHouse offers hourly and month-to-month SSL installation and server hardening engagements with no long-term contract required, so you can validate the service before committing to an annual plan.
SSL installation for a SaaS billing platform is only as good as its renewal automation and audit trail. If your certificate strategy still depends on someone remembering to run a script before expiry, it's time to move to a managed approach built for multi-tenant, PCI-scoped infrastructure.